What was done
Identity proven four ways, all modern hardening mapped, 166 procedures recovered, and a checked verdict that the binary shows no trojanized code.
A static reverse engineering of the Ubuntu netcat-openbsd 1.234-1 binary with the REA agent and Ghidra 12.1.4. The work never executes the program, and every claim in the report points to a committed artifact.
How it was done
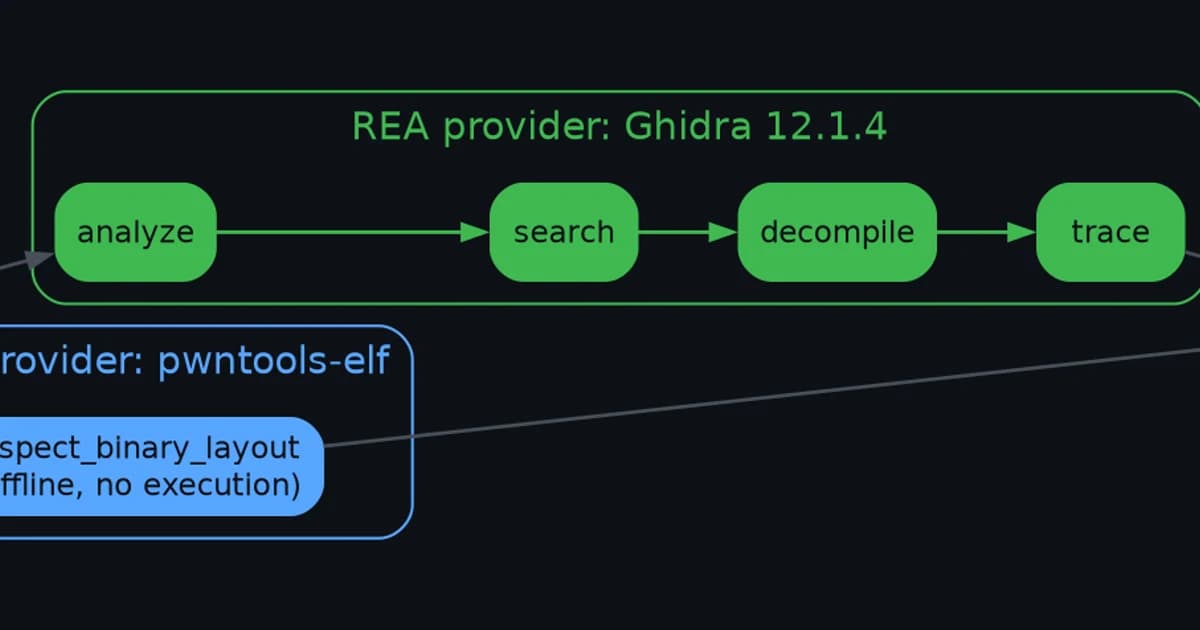
The workflow pins the target by SHA-256 and build ID, confirms the Debian package note and the version banner against the upstream package, and walks the stripped PIE manually: embedded strings, the full option table, imported symbols and hardening features such as full RELRO, stack canary and CET. Ghidra decompilation is then reconciled by REA into a function map with 24 helpers around main and pseudocode for the recovered procedures.
Results
The analysis confirms the binary matches the unmodified Ubuntu package by the four independent checks it claims, catalogues its capabilities and imports, and records in the security notes that no evidence of custom, backdoored or trojanized code was found. Limits and confidence levels are stated openly, and the repository includes a reproduce section so the walk can be repeated on the same SHA-256 sample.